Repair Shop Data Security: How to Protect Customer Data & Build Trust
Why Repair Shop Data Security Matters
Repair shop data security is the set of habits that protect the photos, documents and passwords on every device a customer hands over, and it is now a reason customers choose one shop over another. Their fear is rarely that the repair will fail; it is that personal data will leak. This blueprint covers intake policies, device access, staff permissions and how to tell customers what you do, without technical jargon, so a secure repair shop becomes part of your brand.
The Repair Shop Data Security Blueprint: A Step-by-Step Guide
Here is a practical, actionable guide to turning data security into your greatest competitive advantage.
Step 1: The Trust Pact: Communicate & Get Consent
Transparency is the first step to building trust. Before you touch a single device, you must have a clear, written policy.
-
Get a Digital Signature: Don’t just rely on a verbal agreement. Have the customer sign a digital work authorization that includes a clear privacy clause. This should state that you will only access the data necessary for the repair and that all personal information will be handled with the utmost confidentiality.
-
Be a Guardian, Not a Browser: Make it a strict policy that technicians are only allowed to access the files and functions of a device that are essential for the repair. No browsing photos, checking emails, or opening social media accounts. Ever.
Step 2: Secure Handling & Data Recovery
A customer may come in for a simple screen repair, but what if the repair fails and they lose their data? Offering a professional data recovery services and a clear data backup policy will save you from a major liability.
-
Backup, Backup, Backup: Before starting a repair, perform a secure data backup of the customer’s device if they’ve requested it. Use a professional tool and a separate, encrypted storage device. Never back up a customer’s data to a general-purpose computer or external hard drive.
-
Use Secure Notes: Your
repair ticket managementsystem should have a secure notes feature on every work order. This is where you can document the customer’s login details, but it must be in a secure, encrypted part of the system that is only accessible to authorized technicians. Never write down passwords on a sticky note.
Step 3: The Professional Workflow
A professional workflow is a secure workflow. The process of the repair itself must reinforce your commitment to security.
-
Clear Workspaces: Designate a clean, organized, and private workspace for each repair. This prevents accidental data leaks or unauthorized viewing of sensitive information.
-
Access Control: Not every employee needs access to every part of your system. Your
BytePhasesoftware should have role-based permissions, ensuring that only senior technicians or managers can access sensitive customer notes or data backups. -
Final Data Sanitation: After the repair is complete and the device has been returned to the customer, you must securely erase any temporary files or data that were created during the repair.
Step 4: The Final Hand-Off
The final moments of the transaction are just as important as the first. A secure and professional hand-off can be the difference between a satisfied customer and a loyal one.
-
Confirm Security: When returning the device, take a moment to reassure the customer that their data was not accessed beyond what was necessary for the repair and that it has been handled with the highest level of care.
-
The Right Tools: A
pos systemthat can provide a detailed, itemized invoice with a clear privacy statement is a simple way to reinforce your commitment. It’s a small detail that can have a big impact on a customer’s perception of your professionalism.
Repair shop data security for staff: logins, offboarding, backups
Most of the steps above protect the customer at the counter. The bigger risk is often internal: who on your staff can open which ticket, whether a technician’s login still works after they leave, and whether last night’s backup ran. Privacy laws set the legal floor, but these controls are plain operations, not a compliance project.
Gaps that build up in an honest shop
- One shared shop password, so you cannot tell who opened a customer’s data until something goes wrong.
- Logins for staff who left months ago, still active because nobody owns offboarding.
- Passwords reused between personal and work accounts, so one phishing email exposes the shop.
- Customer devices left unlocked on a shared bench where any staff member or visitor can pick one up.
Four rules your team can actually follow
- One login per person, with access by role: front desk sees contact details and status, technicians see the jobs assigned to them, managers see everything.
- Offboard the same day. When someone leaves, their account is disabled before the end of the shift, not when someone gets round to it.
- Back up before any repair that carries a real risk of data loss, to encrypted, dedicated storage.
- Keep a record of who touched what, so the question “who accessed this customer’s data” always has an answer.
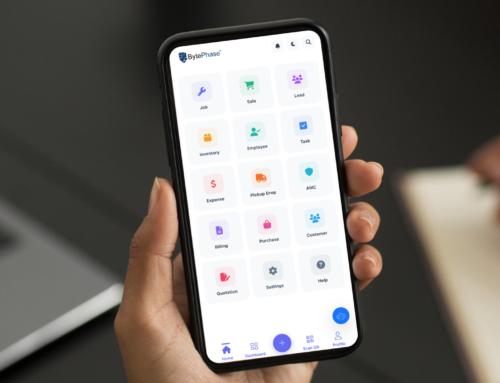
The hard part is enforcing this without an IT person on staff, which is why the system that runs your tickets should enforce it for you. In BytePhase repair ticket management, each staff member has their own login, every action on a job is recorded in an activity log, and business data is encrypted at rest and backed up automatically every day. Customer messages go out through the platform’s own notification channels rather than personal email or chat threads.
The BytePhase Advantage: The Platform for Trust
Building a secure and trustworthy repair business is nearly impossible to do manually. You need computer repair shop software that enforces your policies and provides a transparent workflow. That’s where BytePhase comes in.
Our platform is designed to be the backbone of a professional, secure repair shop.
-
Digital Consent & Work Orders: Our system allows you to create customizable work orders that include your data privacy agreement and require a digital signature from the customer, providing an auditable record for every repair.
-
Secure & Encrypted Notes: Our secure notes feature ensures that sensitive customer information is never stored in plain text or on a physical piece of paper.
-
Audit Trails: BytePhase provides a clear history of every action taken on a repair ticket, so you know exactly who accessed what and when, ensuring accountability and peace of mind.
In a competitive market, a commitment to your customers’ data security is not just a policy; it’s a promise. By implementing a secure and professional workflow, you transform your business from a simple computer service and repair shop into a trusted partner, and that is a brand that will stand the test of time.
Quick Checklist: Is Your Repair Shop Data-Secure?
Run through this list before you call your data security policy complete:
-
Customers sign a digital work authorization with a clear privacy clause before you touch their device.
-
Technicians access only the files and settings needed for the repair — nothing else.
-
Backups, when requested, go to encrypted, dedicated storage, never a shared general-purpose drive.
-
Passwords and access notes live in an encrypted, permission-gated field, never on paper or in plain text.
-
Role-based access limits sensitive customer notes and backups to senior technicians or managers.
-
Temporary files created during the repair are wiped before the device is returned.
-
Every hand-off includes a spoken or written confirmation of what was, and wasn’t, accessed.
None of this has to be manual. BytePhase bakes consent capture, secure notes, role-based access, and audit trails into every repair ticket, so secure handling is the default, not an afterthought. Try BytePhase free for 15 days and see how much easier it is to run a repair shop your customers trust.
Want the policy enforced by the software? BytePhase’s role-based permissions decide who can see customer contact details, payments and device photos, and every action is logged. Start a 15-day free trial and run it against your own jobs.